Verify.Cli GitHub Action
A GitHub Action for doing snapshot testing against files directly in your workflow
I’ve previously written about the command line tool I created for snapshot testing files without needing a unit test framework - Verify.Cli.
I’ve been making good use of this tool as I continue to make changes and improvements to my blog. The underlying “engine” of my blog lives in my astro-blog-engine repo, and it contains a small subset of my blog posts that I use for testing any changes before merging to my full blog repo. The latter repo is private.
Up until now I’ve had these wired up in my blog engine repo’s GitHub Actions workflow like this:
      - name: Verify post
        id: verify_post
        if: github.event_name == 'pull_request' || github.repository == 'flcdrg/astro-blog-engine'
        run: docker run --rm --user "$(id -u):$(id -g)" -v $PWD:/tmp flcdrg/verify-cli --file /tmp/dist/2025/07/azure-pipeline-template-expression.html --verified-dir /tmp/verified --scrub-inline-pattern '(?<prefix>")/_astro/[^"]+(?<suffix>")' --scrub-inline-pattern '(?<prefix>title=")[^"]+(?<suffix>")' --scrub-inline-remove ' data-image-component="true"' --scrub-inline-pattern '(?<prefix>meta name="generator" content="Astro v)[\d\.]+(?<suffix>")' --verbosity detailed

      - name: Diff post if error
        if: failure() && steps.verify_post.outcome == 'failure'
        run: |
          ls -al verified/
          echo ""
          diff -u verified/azure-pipeline-template-expression.html.verified.html verified/azure-pipeline-template-expression.html.received.html
Just this week I discovered I’d accidentally messed up the Tags page on my blog. A recent change had mixed up the tag name and the count for the number of pages with that tag, which caused all the links to be broken.
I realised that page didn’t have a covering snapshot test in the engine repo, so some copy/paste ensued. In doing that it occurred to me that I really should extract out the common logic and make it a reusable GitHub Action. So that’s what I’ve done.
verify-cli is now listed in the GitHub Actions marketplace, and the source is at https://github.com/flcdrg/verify-cli-action
I can now simplify my blog’s workflow file by using this new action:
      - name: Verify post
        if: github.event_name == 'pull_request' || github.repository == 'flcdrg/astro-blog-engine'
        uses: flcdrg/verify-cli-action@v1
        with:
          file: dist/2025/07/azure-pipeline-template-expression.html
          verified-directory: verified
          working-directory: .
          scrub-inline-pattern: |
            (?<prefix>")/_astro/[^"]+(?<suffix>")
            (?<prefix>title=")[^"]+(?<suffix>")
            (?<prefix>meta name="generator" content="Astro v)[\d\.]+(?<suffix>")
          scrub-inline-remove: ' data-image-component="true"'
          verbosity: detailed
Failing example
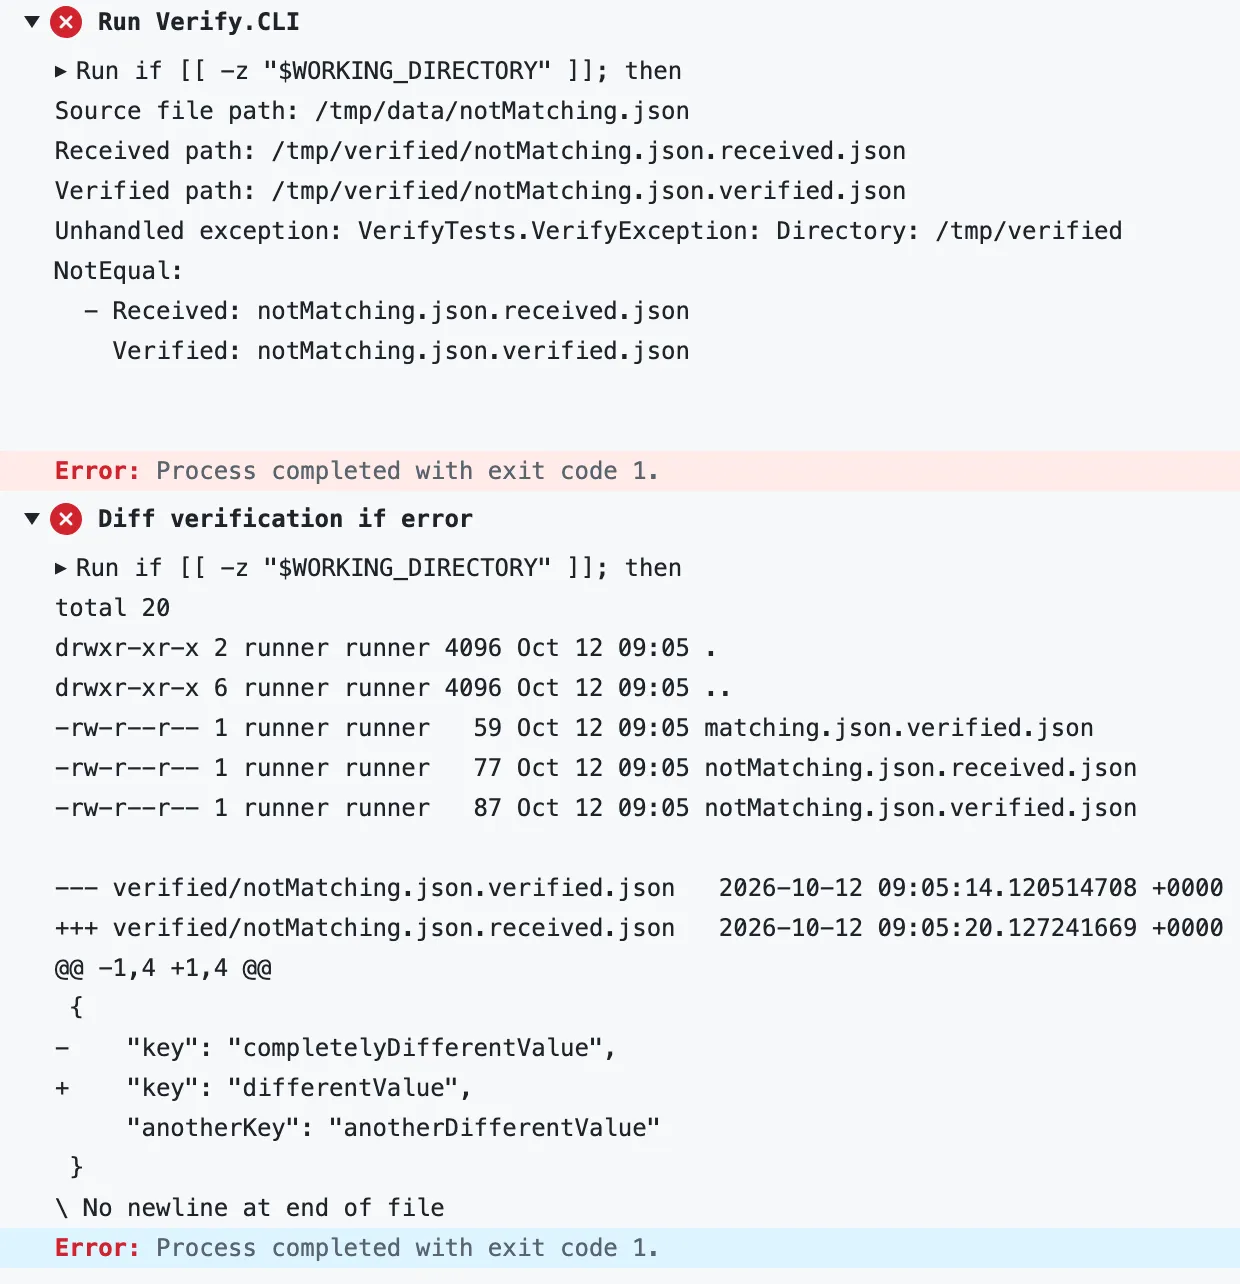
Here’s an example (based on the test workflow in the verify-cli-action repo) to show what it looks like if the received file doesn’t match the verified file
The workflow step is similar to this:
      - name: "Match in separate verified directory - not matching"
        uses: flcdrg/verify-cli-action@v1
        with:
          file: "data/notMatching.json"
          working-directory: "samples/separate-verified"
          verified-directory: "verified"
With this result:
If you need to ensure that a file’s contents match a known state (and need to ignore specific text like timestamps), but be alerted by a failing GitHub Actions workflow if it changes (and see what those changes are), then this action might be just the thing.